GitHub Actions, Argo CD, Helm, and automated release paths — from commit to production with repeatable CI/CD workflows.
Vazeer BashaShaik
AWS Certified Solutions Architect DevOps AWS Cloud Engineer
Verified AWS Credential
AWS Certified Solutions Architect — Associate
About Me
DevOps & AWS Cloud Engineer — secure, automated delivery from code to production.
Professional Summary
AWS Certified Solutions Architect — DevOps & AWS Cloud Engineer focused on automated delivery on AWS.
I build EKS GitOps pipelines, serverless architectures, event-driven systems, and Terraform infrastructure. Every project includes architecture diagrams and documented tradeoffs.
What I Bring
Docker, Kubernetes (EKS), Terraform, and AWS platform services wired into secure, scalable delivery pipelines.
Three focused security repositories — Network Firewall threat detection, IAM Access Analyzer reviews, and Lambda-driven security group automation.
Prometheus, Grafana, CloudWatch, and fault-tolerant design — metrics, alerting, and resilience built into every delivery path.
Delivery Pipeline
Secure CI/CD from GitHub to CloudFront — the pipeline running this site.
GitHub OIDC federated auth
Least-privilege IAM role
Private S3 + CloudFront OAC
AWS production + GitHub Pages backup
Authenticate
GitHub Actions
Merge workflow
GitHub OIDC
Federated trust
AWS IAM Role
Least privilege
STS Credentials
Short-lived
Amazon S3
Private origin
Invalidation
Edge refresh
CloudFront
CDN + OAC
Live Portfolio
vazeershaik.in
01
Trigger on Merge
A push to main starts the GitHub Actions workflow — the single source of truth for AWS production and GitHub Pages backup.
02
Federated Authentication
GitHub OIDC assumes an AWS IAM deployment role. STS issues temporary credentials per run — no permanent access keys or GitHub Secrets.
03
Deploy to Private S3
Static assets sync to a private S3 bucket with stale-file cleanup. CloudFront OAC is the only read path to the origin.
04
Global Edge Delivery
CloudFront invalidation refreshes the CDN cache and publishes the live portfolio worldwide within seconds.
AWS Cloud Quest
Four hands-on tracks with independent Credly verification.
AWS Cloud Quest Solutions Architect
Trained — Hands-on cloud architect
Verify on CredlyAWS Cloud Quest Security
Trained — Hands-on cloud security
Verify on CredlyAWS Cloud Quest Serverless
Trained — Hands-on serverless
Verify on CredlyAWS Cloud Quest Networking
Trained — Hands-on cloud networking
Verify on CredlyEngineering Standards
The standards applied to every build and delivery path here.
Every Decision, Documented
Cost, availability, and complexity tradeoffs written for each architecture — so design intent survives beyond the initial build.
Built for Failure First
Multi-AZ placement, autoscaling thresholds, and fault boundaries defined before go-live — not patched in after an incident.
Perimeter Public, Core Private
CloudFront and API Gateway expose only the edge — application and data tiers stay in private subnets with no direct inbound path.
GitOps & Infrastructure as Code
Terraform modules, remote state locking, and GitOps-style promotion — environments advanced through version control, not console changes.
Featured Builds
Twelve AWS builds across DevOps, Serverless, IaC, Security, and core AWS architecture — each with diagrams, tradeoffs, and GitHub repos.
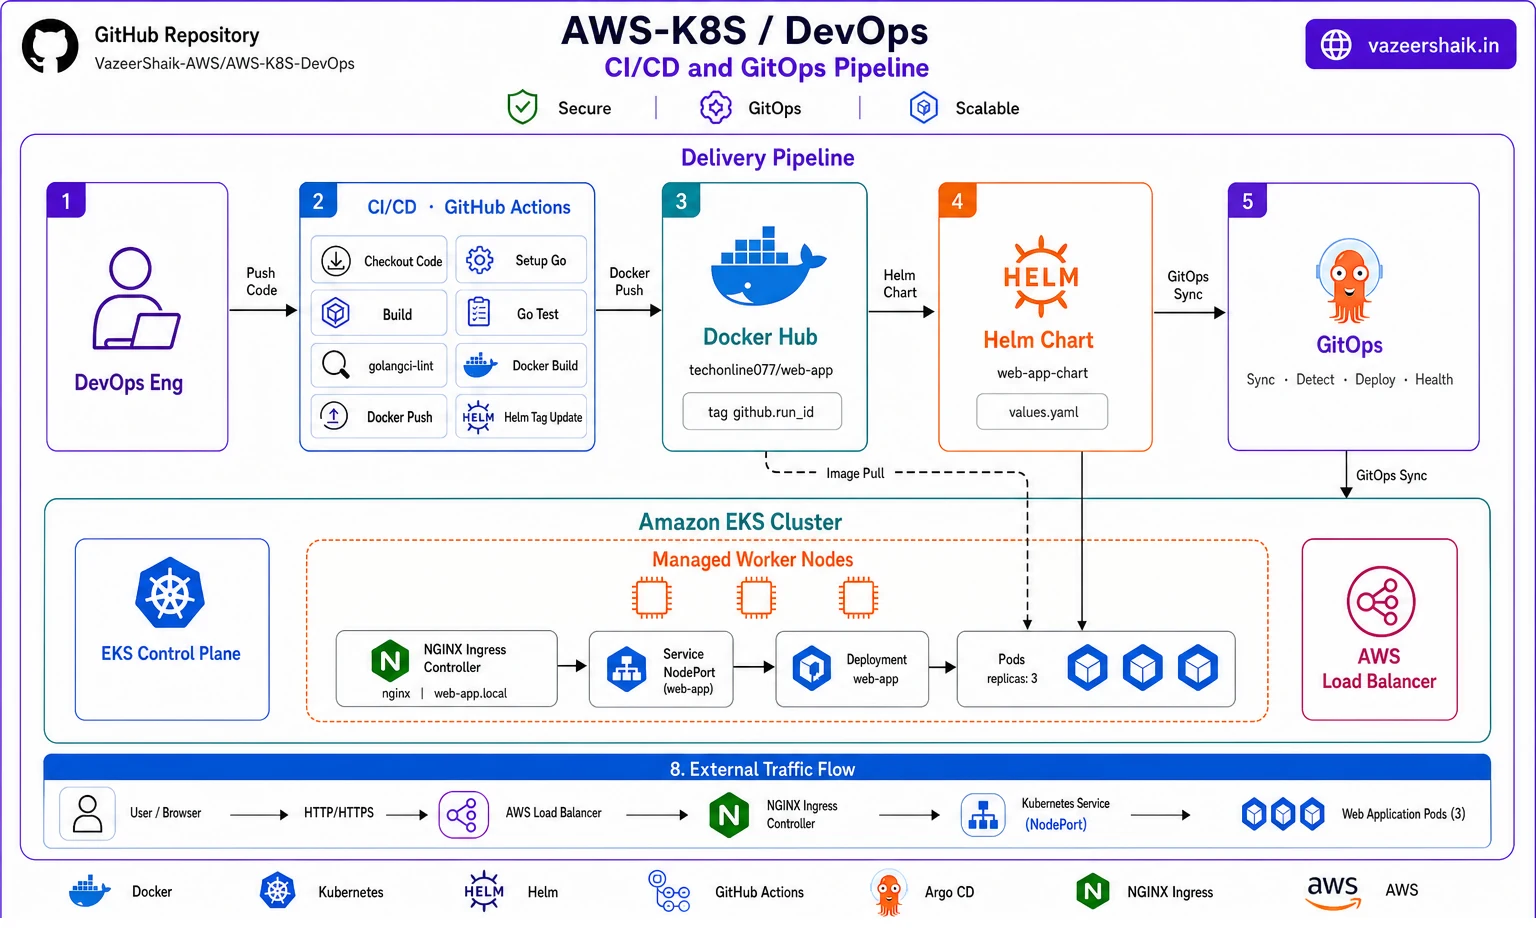
AWS EKS DevOps — Go Web App GitOps


End-to-end GitOps delivery for a Go web app on Amazon EKS — CI, Docker, Helm, and Argo CD with NGINX Ingress.
Key Features
- GitHub Actions CI: Go build, tests, golangci-lint, and Docker image publish
- Helm chart with automated image tag updates wired into GitOps
- Argo CD reconciles Amazon EKS to the Helm chart in Git
- NGINX Ingress and AWS Load Balancer for external access, not per Pod
- Multi-stage Distroless Docker image for consistent laptop-to-EKS runs
Tradeoffs
GitOps and Helm add deployment flexibility but introduce cluster sync lag and chart versioning overhead compared to direct kubectl deploys.
Services Used:
Amazon EKS
GitHub Actions
Docker Hub
Helm
Argo CD
NGINX Ingress
AWS Load Balancer
Go
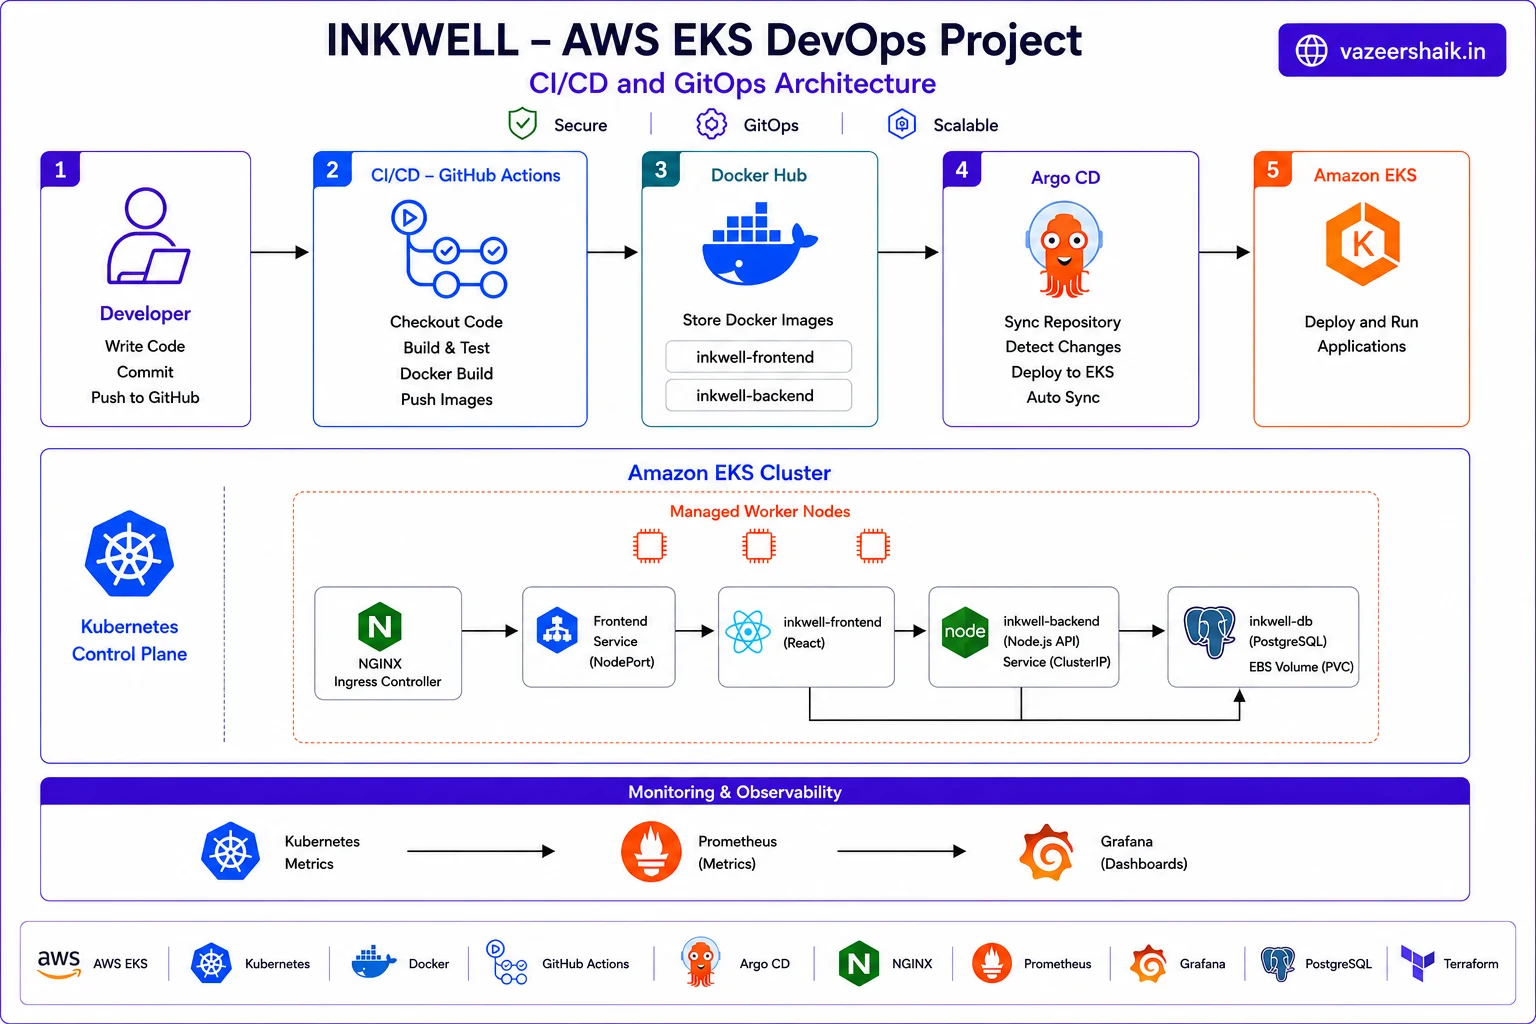
InkWell — AWS EKS DevOps
3-tier blog platform on Amazon EKS with DevOps CI, Terraform, GitOps, and Prometheus/Grafana observability.
Key Features
- Terraform-provisioned EKS Auto Mode cluster with envelope encryption and audit logging
- Kubernetes NetworkPolicies for zero-trust pod communication
- Container security contexts: non-root, read-only root filesystem, dropped capabilities
- Prometheus and Grafana observability for cluster and workload metrics
Tradeoffs
Layered security scanning and NetworkPolicies improve posture but lengthen CI runtime and add operational complexity.
Services Used:
Amazon EKS
Terraform
GitHub Actions
Docker Hub
Prometheus
Grafana
NGINX Ingress
AWS · Architecture
Multi-Tier Architecture on AWS
Highly available web, application, and database tiers on AWS — Multi-AZ subnets, Auto Scaling, ALB, and private RDS.
Key Features
- VPC with public and private subnets across multiple Availability Zones
- Application Load Balancer routing traffic to an Auto Scaling web tier
- App tier in private subnets with controlled security group access
- Amazon RDS Multi-AZ for durable, isolated database storage
Tradeoffs
Multi-tier separation improves resilience and blast-radius control but adds networking and operational complexity versus a single-tier design.
Services Used:
IaC · Kubernetes
EKS Cluster with Custom VPC — Terraform
Production-grade Amazon EKS cluster in a custom VPC — Terraform IaC with multi-AZ subnets, managed node groups, IRSA, and CloudWatch logging.
Key Features
- Custom VPC with public & private subnets across multiple AZs
- NAT Gateway for secure outbound access from private worker nodes
- Managed Node Group with auto-scaling EC2 worker nodes
- IAM Roles for Service Accounts (IRSA) for pod-level permissions
Tradeoffs
Terraform IaC enables full repeatability but adds state management overhead.
Services Used:
Infrastructure as Code
IaC · Multi-Env
Multi-Environment AWS Infrastructure — Terraform
Provisioned isolated VPC and EC2 web servers across dev, stage, and prod using Terraform Workspaces. Each environment uses dedicated networking, environment-specific variables, and remote state in S3 with DynamoDB locking.
Key Features
- Terraform Workspaces for dev, stage, and prod isolation
- Dedicated VPC, public subnet, and EC2 web server per environment
- Environment-specific variables with unique CIDR blocks per workspace
- Remote state in S3 with DynamoDB locking for safe deployments
Tradeoffs
Workspaces simplify multi-environment deploys but require careful workspace and variable selection.
Services Used:
IaC · State Backend
Terraform S3 Remote State with DynamoDB Locking
Built a production-style Terraform remote backend using S3 for state storage and DynamoDB for apply locking. Includes a dedicated state-backend stack and workspace-based dev/prod deployments with SSM Parameter Store.
Key Features
- S3 remote state with versioning, encryption, and access controls
- DynamoDB table for Terraform state locking during concurrent applies
- Separate dev and prod workspaces with environment-specific variables
- SSM Parameter Store for workspace-isolated resource deployment
Tradeoffs
Remote state enables safe team collaboration but adds backend infrastructure to provision before workloads deploy.
Services Used:
Serverless & Events
Serverless · Messaging
Serverless Messaging — SNS, SQS & Lambda
Built a serverless messaging pipeline to ensure reliable and asynchronous communication between services. Designed to handle traffic spikes without data loss.
Key Features
- Decoupled architecture
- Event-driven auto-scaling with zero idle cost
- Reliable message delivery with durable queues
- CloudWatch visibility on queue depth and processing latency
Tradeoffs
Adds latency and requires handling message duplication and ordering.
Services Used:
Serverless · Events
Event-Driven — API Gateway, EventBridge & Lambda
Designed an event-driven system to enable asynchronous communication and reduce tight coupling between services, improving scalability and flexibility.
Key Features
- Decoupled event-driven design
- Efficient high-volume event handling
- Resilient, independently scalable consumers
- Observability hooks for tracing events across services
Tradeoffs
Debugging and tracing events becomes more complex. Eventual consistency.
Services Used:
Security & Edge
Security · Network
Threat Hunting with AWS Network Firewall
Implemented deep packet inspection and traffic filtering to detect and control malicious network activity.
Enhances network security, but increases latency and requires complex rule management.
Automation · Lambda
Security Group Automation Lambda
Automated dynamic security group rule updates to enforce consistent network access and reduce manual intervention.
Improves operational efficiency, but incorrect automation logic can lead to unintended access or service disruption.
Security · VPC
VPC Network Access Analyzer
Analyzed network access paths to identify unintended exposure and validate secure connectivity across resources.
Provides visibility into access paths, but requires manual remediation and does not enforce changes automatically.
CDN · Edge
CloudFront Dynamic Content Acceleration
Accelerated global content delivery using CDN edge locations and caching strategies to reduce latency and improve performance.
Improves global performance, but adds cache invalidation complexity and additional cost.
Platform Stack
AWS platform services and DevOps delivery tooling — from infrastructure to observability.
CI/CD
Docker
Kubernetes
AWS
Terraform
Prometheus
Grafana


Platform
AWS Services
- Compute & Scaling
- Amazon EC2, AWS Lambda, Auto Scaling
- Load Balancing & API
- Application Load Balancer, Network Load Balancer, Amazon API Gateway
- Messaging & Events
- Amazon SNS, Amazon SQS, Amazon EventBridge
- Network & CDN
- Amazon VPC, NAT Gateway, Security Groups, Amazon CloudFront, Amazon S3
- Database & Storage
- Amazon RDS, Amazon DynamoDB, Amazon Aurora
- Security & Observability
- AWS IAM, AWS CloudTrail, AWS CloudWatch, AWS Network Firewall

DevOps
Delivery & Orchestration
- CI/CD & GitOps
- GitHub Actions, Argo CD, Helm charts, Git-driven deploys
- Containers & Orchestration
- Docker, Kubernetes (EKS), NGINX Ingress, AWS Load Balancer
- Infrastructure as Code
- Terraform, S3 remote state, DynamoDB locking, workspaces
- Observability
- Prometheus, Grafana, AWS CloudWatch, metrics & alerting
- Automation & Security
- Lambda automation, IAM least privilege, secrets-aware pipelines
Let's Talk
Open to full-time and hybrid DevOps & AWS Cloud Engineering roles.
Open to Opportunities
Built for
Built for
what's next.
Open to full-time and hybrid opportunities in DevOps and AWS Cloud Engineering.
Email
vazeershaik.aws@gmail.com
GitHub
VazeerShaik-AWS
LinkedIn
vazeer-shaik
Open to full-time & hybrid DevOps & AWS cloud roles
Typically responds within 24 hours